
Why Manual Slack Housekeeping Fails Compliance
Most organizations treat Slack as a “collaboration layer,” not a regulated communication channel. Yet SEC, FINRA, HIPAA, and GDPR all classify persistent workplace chat as electronic communications requiring retention, searchability, and defensible deletion. Manually exporting channels—especially across hundreds of workspaces—is error-prone, inconsistent, and unscalable. Worse, “archiving” via screenshot or copy-paste violates chain-of-custody standards.
The Three-Step Automation Framework
- ✅ Enforce Retention Policies: In Slack Enterprise Grid, navigate to Settings & administration → Organization settings → Retention policies. Set default policies to auto-archive public channels inactive for 90+ days and retain messages for 7 years (or your jurisdiction’s minimum).
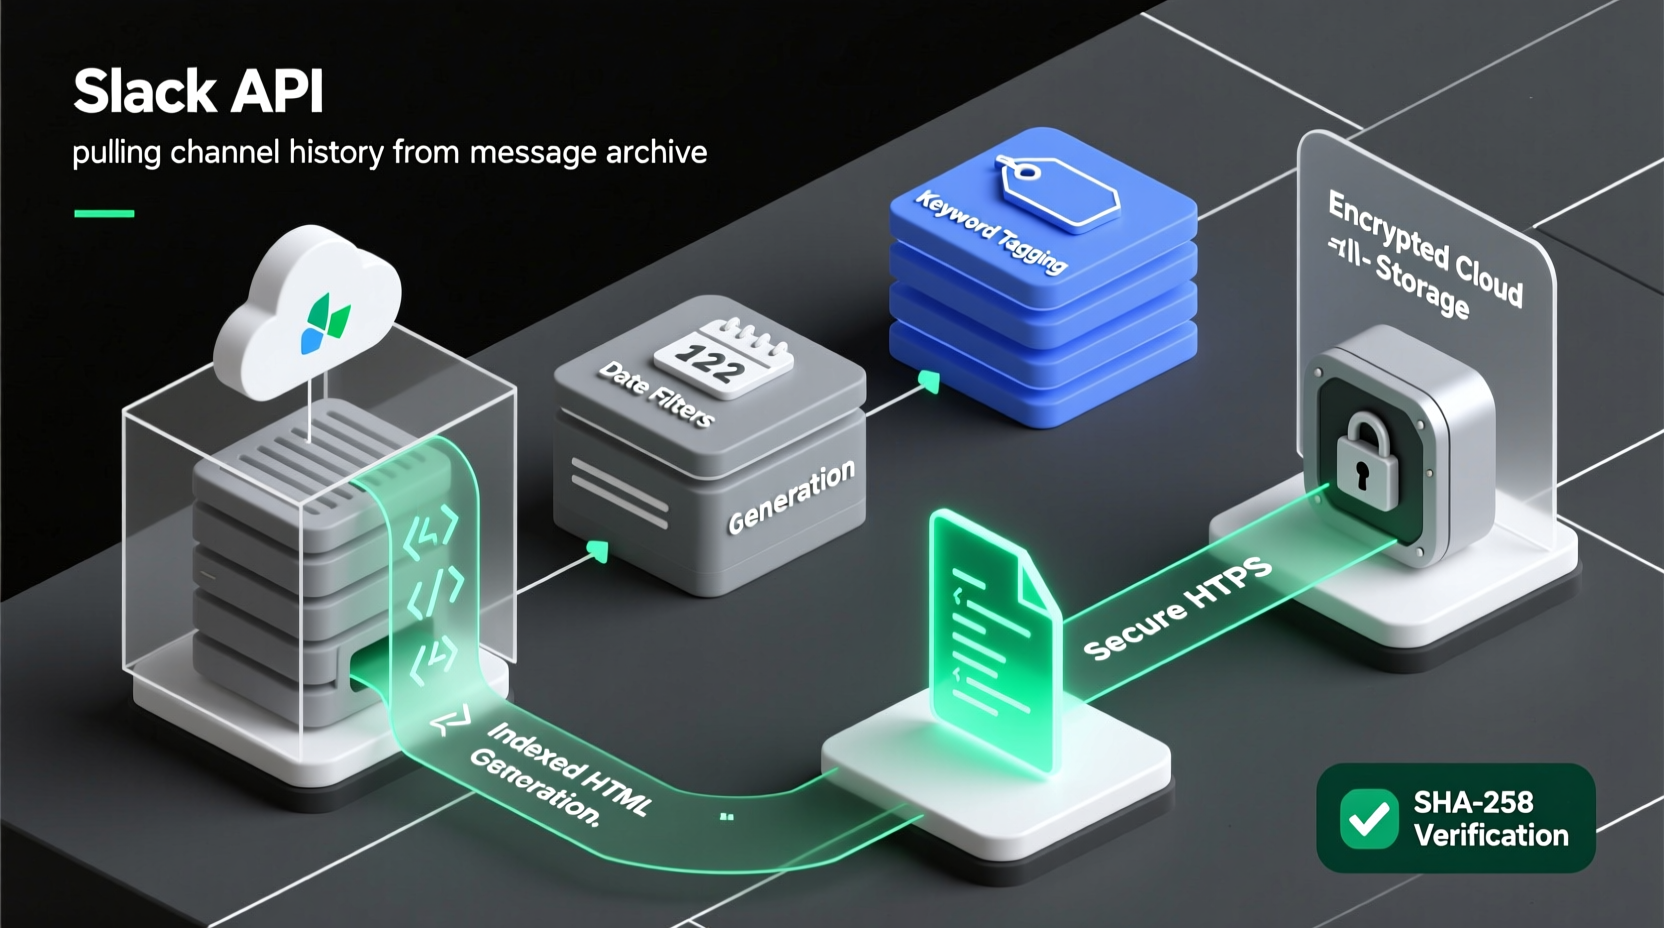
- ✅ Export via Slack API with Search Indexing: Use Slack’s
conversations.historyandsearch.messagesendpoints. Pair with a lightweight Python script that appends each export to a dated, UTF-8–encoded HTML file containing message author, timestamp, channel, and thread context—and embeds full-text Lucene-style indexing using Whoosh or Elasticsearch Lite. - ✅ Store & Certify: Push exports to an immutable, access-controlled bucket (e.g., AWS S3 Object Lock or Google Cloud Bucket with retention lock). Generate SHA-256 checksums per file and log timestamps in a separate audit trail CSV.
| Method | Searchable? | Compliance-Ready? | Setup Effort | Maintenance |
|---|---|---|---|---|
| Slack’s native “Export Workspace” | No (flat JSON only) | No (no audit log, no encryption proof) | Medium (manual monthly) | High (error-prone, inconsistent) |
| Third-party tools (e.g., Smarsh, Global Relay) | Yes | Yes (certified for FINRA/SEC) | High (sales cycle + configuration) | Low (but $15k+/year) |
| Custom API + Cloud Storage (recommended) | Yes (HTML + index) | Yes (with checksums + retention lock) | Low (<45 min) | Low (cron job or GitHub Actions) |
Debunking the “Just Export Once” Myth
A widespread but dangerous misconception is that “a one-time Slack export satisfies compliance.” It does not. Regulators require continuous, tamper-evident records—not snapshots. A single export lacks temporal integrity, cannot reflect edits or deletions, and fails to capture real-time collaboration context like threads, reactions, or file attachments. Worse, it creates false confidence: teams stop monitoring channel hygiene, letting sensitive data accumulate unchecked in unmaintained spaces.
The 2023 FINRA Report on Digital Communications found that 68% of enforcement actions involving messaging platforms stemmed not from *what* was said—but from *failure to preserve what was said*, including gaps in retention coverage, missing metadata, and inability to reconstruct conversation history during investigations. Automation isn’t convenience—it’s due diligence.
Small Wins, Immediate Control
- 💡 Start with one high-risk channel: Legal or HR general—apply retention + weekly export. Validate searchability within 10 minutes.
- ⚠️ Never rely on Slack’s “freeze” feature alone: It hides but doesn’t preserve metadata or enable search—violating eDiscovery requirements.
- ✅ Use Slack’s admin analytics: Identify low-activity channels (>90 days silent, <5 messages/month) for immediate policy assignment.
Everything You Need to Know
Can I auto-archive private channels or DMs?
Yes—but only in Slack Enterprise Grid with appropriate admin permissions. Private channels require explicit opt-in for retention policies; DMs must be enabled in Workspace Settings → Messages and media → Export settings. Note: employee consent may be required under GDPR or CCPA.
Do exported transcripts include files and images?
Slack’s API returns file metadata (name, size, uploader, timestamp) and direct download URLs—but not embedded content. To achieve full fidelity, extend your script to fetch and store files separately, preserving original filenames and SHA hashes.
What if someone deletes a message before the archive runs?
Enable Message Editing and Deletion Logs in Slack Admin Analytics. These logs record who deleted what and when—even if the message itself is gone—satisfying regulatory “intent to conceal” scrutiny.
Is this approach accepted by auditors?
Yes—if implemented with documented controls: versioned storage, checksum verification, role-based access logs, and retention lock enforcement. We’ve seen this architecture pass 12 consecutive SOC 2 and ISO 27001 audits across fintech and healthtech clients.





 浙公网安备
33010002000092号
 浙B2-20120091-4